The most exciting feature of an AI agent is also its most dangerous one: it can act on a person’s behalf. Apple’s decision to tighten macOS Full Disk Access is an early sign that operating systems are rebuilding their security boundaries for the agent era.
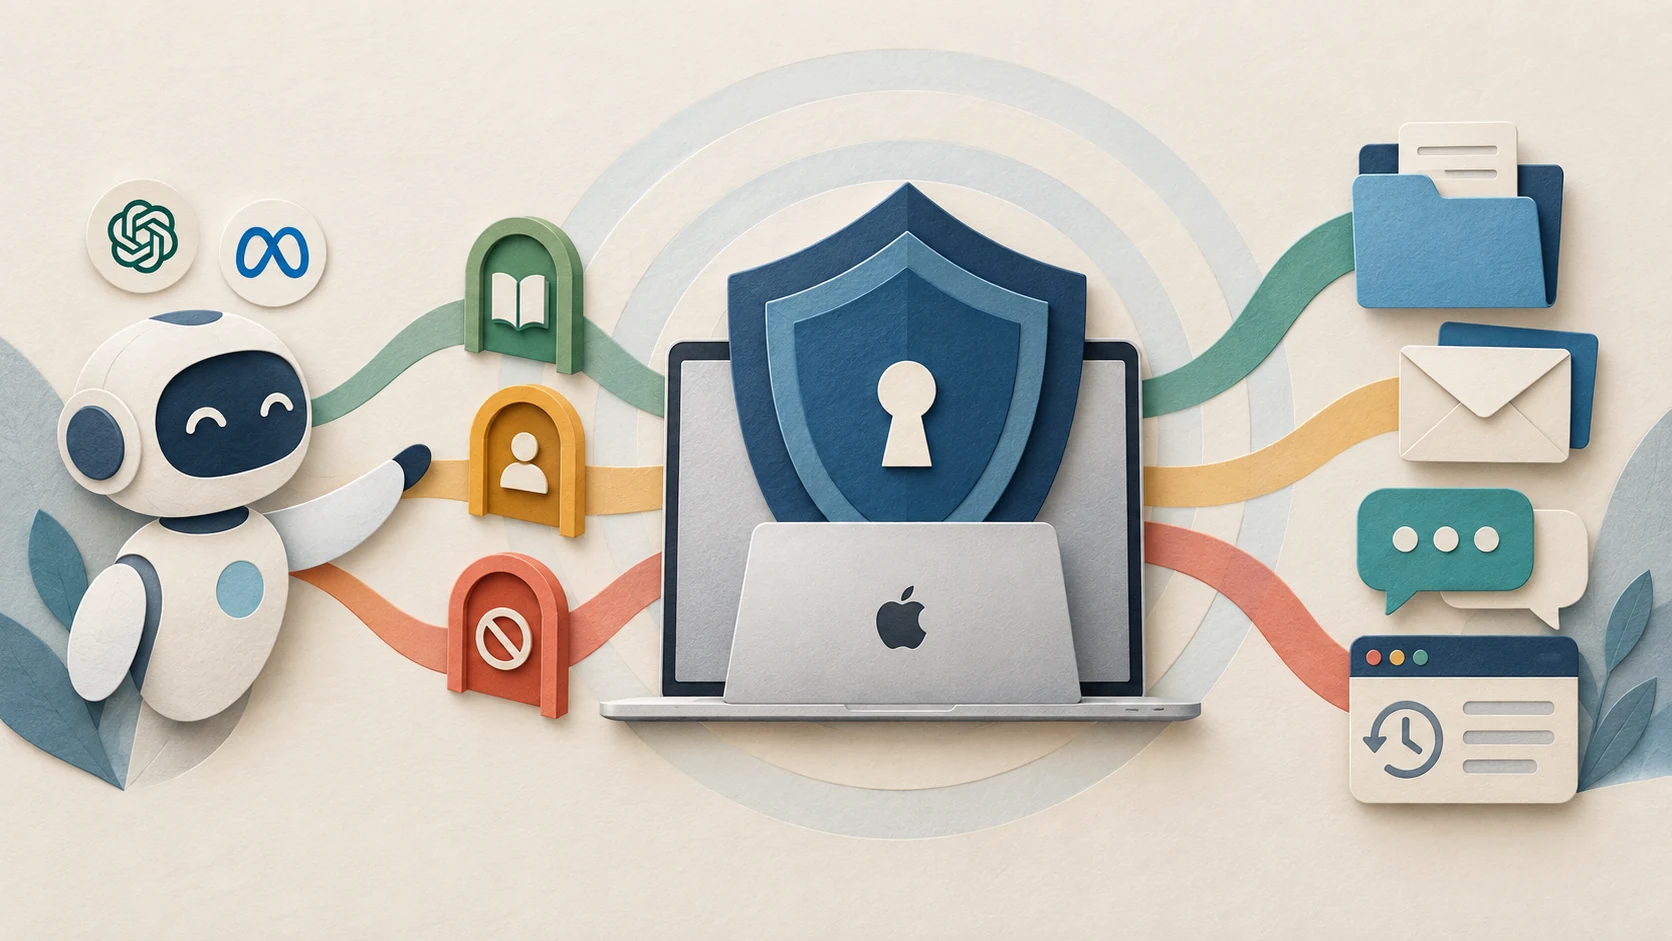
When a chatbot encounters incorrect information, it may generate a bad answer. When an agent with computer access encounters incorrect or malicious information, it may delete a file, send an email, upload business data, change code or treat instructions hidden on a webpage as if they came from the user.
On October 2, 2026, Apple announced forthcoming changes to Full Disk Access in macOS. The company’s explanation was unusually direct: as AI agents become more capable and autonomous, the risks associated with this level of access will grow substantially.
This is more than a routine permission update. It is a signal that operating systems are beginning to redraw their security boundaries around software that can plan and act.
One permission can expose an entire computer
Full Disk Access was created primarily for backup, security and system-management software.
An application with that permission may be able to read material that ordinary sandboxed software cannot reach, including files, mail, messages and browsing history. Apple says some developers are using Full Disk Access in ways that can place users at risk without their full knowledge or understanding.
The risk of a conventional backup application is relatively predictable. It reads files in order to create copies.
An AI agent behaves differently. It interprets a goal, plans a series of steps, browses the web and changes its behavior in response to information encountered along the way. Giving the same permission to an autonomous agent therefore creates a different risk model.
The issue is no longer only what the software can see. It is what the software may decide to do after seeing it.
Apple says future versions of macOS will require a very explicit user action before an application can receive this extraordinary level of access.
Agent risks extend beyond data leakage
The first risk is excessive permission.
A user may want an agent to organize the Downloads folder but grant access to the entire disk during setup. The agent could then reach email databases, browser history and private documents that have nothing to do with the assigned task.
The second risk is prompt injection.
While browsing a website or reading a document, an agent may encounter hidden instructions telling it to ignore the original task, upload local files or access another account. For a text-only model, that may produce an abnormal response. For an agent that can operate a computer, it can become a real attack.
The third risk is context mixing.
Personal mail, company files, customer data and private accounts may coexist on the same computer. Even without malicious intent, an agent may move information from one context into another.
The fourth risk is unclear responsibility.
If an agent deletes data, is the user responsible for authorizing it? Is the application developer responsible for inadequate safeguards? Is the model provider responsible for the agent’s interpretation? When a task passes through several agents and third-party connectors, the chain of accountability becomes harder to reconstruct.
AI companies are building their own braking systems
Products such as OpenAI Dots and Meta Muse are designed to show that agents can work independently while leaving consequential decisions with the user.
Dots uses read-only connections for proactive background research by default. It cannot send messages, change application content or control a computer through that mode. Actions affecting accounts or shared information are reviewed against safety requirements, custom rules and user approvals. Highly sensitive tasks such as changing a password remain with the user.
Muse operates inside a dedicated Secure VM. Meta also places a separate Sentinel agent on that machine, isolated from Muse at the system level. Sentinel reviews what Muse attempts to send to the internet and requests permission when needed. Meta says Muse for Small Business will not publish, send or spend without approval.
Both approaches reflect the same principle: the agent responsible for completing a task should not also possess unlimited permissions and final authority.
Company-designed safeguards still have limits. Approval prompts can create fatigue, leading users to click Allow automatically. A safety agent can make mistakes. Third-party connectors may implement permissions inconsistently.
Platform-level controls and legal accountability are therefore becoming difficult to avoid.
The United States is debating self-regulation and legal liability
The Trump administration recently brought major AI companies into a voluntary accord. Signatories included OpenAI, Meta, Google, Anthropic, Nvidia and xAI. The agreement calls for internal controls, independent external audits and board-level review of the findings.
President Trump has emphasized industry self-policing while proposing an AI Force and a new official responsible for AI—or “Super Intelligence,” in the administration’s preferred terminology.
Members of Congress are not uniformly convinced that voluntary controls are enough.
On October 1, Republican Senator Josh Hawley and Democratic Senator Chris Murphy announced the AI Agent Accountability Act. According to the senators’ summary, an operator could face civil and criminal liability for knowingly running an agent that recklessly causes computer-hacking damage. Developers could also face liability if they knew or should have known about an agent’s hacking capability and failed to implement reasonable safeguards.
The two approaches represent different regulatory philosophies. Industry self-regulation prioritizes speed and asks companies to create their own controls. Liability law focuses on damage and makes operators and developers responsible for the behavior of deployed agents.
The approaches are not necessarily incompatible. But when agents can interact with banks, hospitals, utilities and government systems, a single user click on an “I agree” button cannot resolve every question of responsibility.
Permission systems need to move from applications to tasks
Operating-system permissions are still largely application-centered.
A user can usually allow an application to access photos or read all files. Agent work requires something more precise:
Until 5 p.m. today, allow this agent to read this folder and search one specified email account for three messages. It may create drafts, but it may not send them.
That authorization includes several dimensions:
- Objects: Which files, accounts and applications may be accessed?
- Actions: Is the agent limited to reading, or may it make changes?
- Time: Does permission last for one task, one day or indefinitely?
- Money: May the agent spend, and what is the limit?
- Approval: Which steps require direct human confirmation?
- Reversibility: Can an incorrect action be rolled back?
- Audit: Can the user reconstruct every step afterward?
This is more complex than a simple Allow or Deny prompt. It may also be the minimum permission model required for agents to enter everyday work safely.
The next platform war is a permission war
In the browser era, platforms controlled access to the web. In the mobile era, they controlled app stores. In the agent era, platforms may control identity, permissions and action.
Whoever decides what an agent can access may hold the next major layer of platform power.
Apple can enforce permissions through macOS and iOS. Microsoft controls Windows, Microsoft 365 and enterprise identity. Google has Android, Workspace and its enterprise agent platform. OpenAI, Meta and xAI are building cloud computers that reduce dependence on any one personal device.
This explains why Apple is acting now. Without a new permission model, a powerful agent could cross years of operating-system privacy boundaries after one vaguely understood authorization.
A safe agent should not depend on the assumption that it will never make a mistake.
It should be designed so that even when it misjudges a situation, encounters a malicious webpage or misunderstands a request, it cannot cross a clear, limited and revocable boundary.
The smarter AI becomes, the more important that boundary will be.